Some companies see cybersecurity as a cost center. We see things a little different. LEARN MORE >
 Experiencing a Breach?

BLOG
The Truth About AI-Enabled Vulnerability Discovery
Claude Mythos and other next-gen AI models are lightning-fast. But the fundamentals haven’t changed.
Key Takeaways
- AI changes the speed, not the rules. Claude Mythos and similar models compress the time it takes to find and exploit vulnerabilities and lower the skill needed to do it.
- The categories of risk are the same. Attackers still rely on exposed services, weak identity and unpatched systems.
- Copy Fail shows the new timeline. A Linux flaw (CVE-2026-31431) that sat undetected for nearly a decade was found by an AI scanner in about an hour and actively exploited within days.
- Unmanaged assets are the real exposure. Microsoft found unmanaged devices involved in more than 90% of ransomware attacks that reached the ransom stage.
- Know what’s actually connected. The gap between your inventory on paper and your live network is your real risk.
- Tarot puts it in one view. Asset intelligence, vulnerability data, threat context and business risk are stitched into one prioritized picture.
There’s been a lot of conversation lately about Claude Mythos and AI-enabled vulnerability discovery.
Here’s a little perspective to help you sort through the noise and focus on what matters.
What Mythos & Other AI Models Actually Alter
The headline is that AI can now discover and chain together vulnerabilities at machine speed. That’s largely true. But it’s worth being precise about what’s actually new here.
AI changes two basic things. It drastically speeds up threat reconnaissance, and it lowers the required skill level for anyone attempting to exploit these vulnerabilities via vibe coding and automated attack chains.
Those are two pretty big things. But still, the fundamentals haven’t changed.
At least not fundamentally.
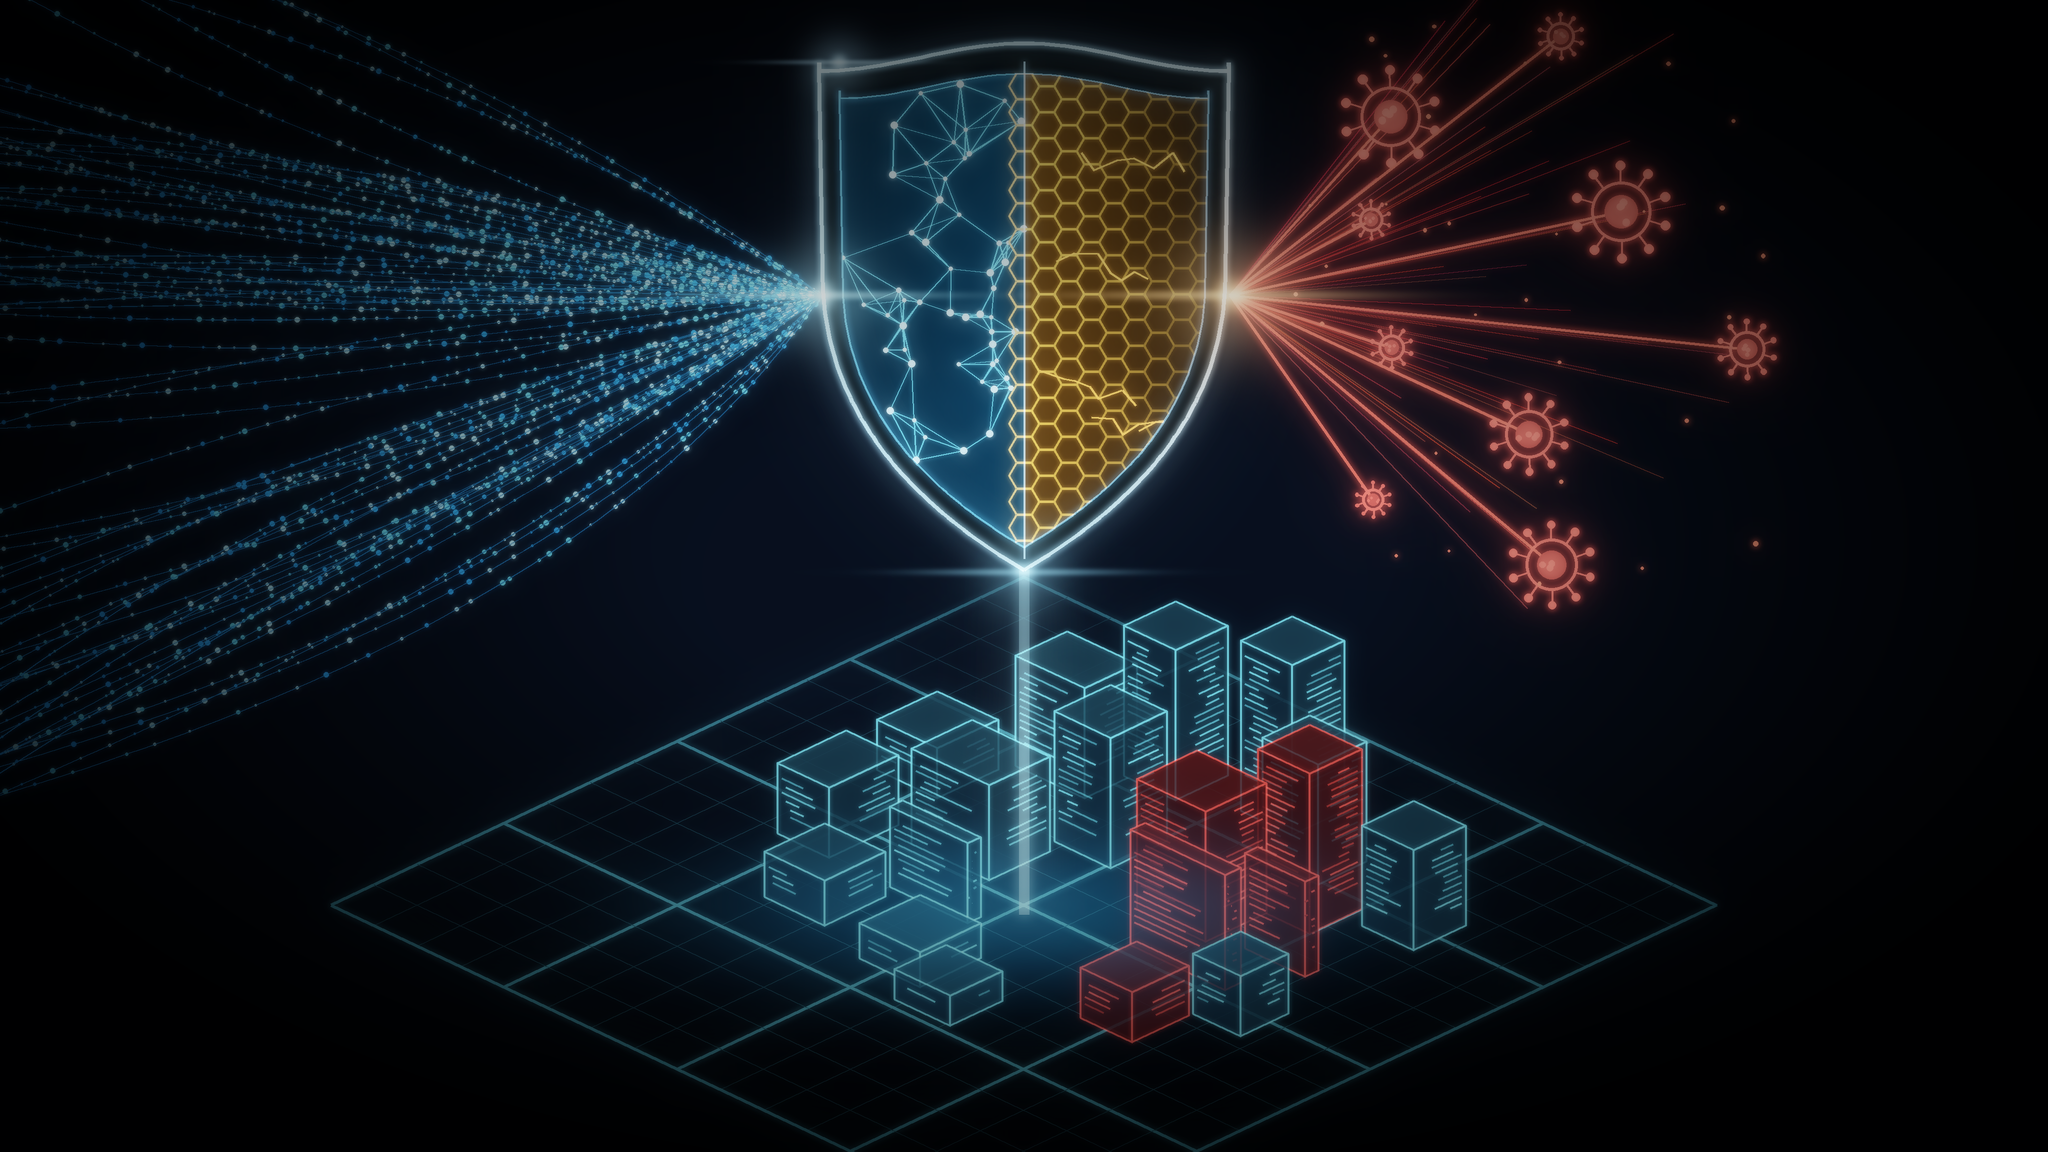
Powerful as it is, AI can still only exploit assets that have been left exposed. Properly hardened systems will still hold up, which means attackers will still rely on the same paths they always have: exposed services, weak identity and unpatched systems.
In summary, the categories of risk are the same ones you’ve been managing for years. It’s just that Mythos and other AI tools have significantly compressed the timeline (and lowered the technical bar) for discovering and exploiting these risks.
The Not-So-Curious Case of Copy Fail
The Copy Fail Linux vulnerability (CVE-2026-31431) is a great example. Disclosed this spring, it lets anyone with basic access to a Linux system take full root control on nearly every major distribution shipped since 2017.
After living under the radar for nearly a decade, it was found by an AI-powered code scanner in about an hour. Within days, CISA added it to its list of actively exploited vulnerabilities.
The patches have since been released, and the remediation is now straightforward, so long as you know where your affected systems are and what versions they’re running.
In other words—you’re fine if you’re following the fundamentals.
But what if you aren’t?
Copy Fail only needs a foothold to cause major trouble. Pair it with a vulnerable web app or a stolen login, and an attacker goes from a low-level account to full control of the server.
Before AI, attackers would have had to do that work themselves: scanning, enumerating, building the chain. That would have bought you extra days, sometimes weeks.
In a post-Mythos world, bad things can happen in minutes.
And this is just one of many examples.
We saw a more recent one with PHP2Shell. Once again, good guys with AI found the flaws first. But this time, the bad guys were right behind them, exploiting the flaws before a patch even existed.
Mythos Gets the Glory. Unmanaged Assets Are the Story.
Every environment has them. The forgotten Linux box. The vendor appliance still running default credentials. The IoT device someone plugged in three years ago. The infamous shadow IT server.
These are exactly the sorts of unmanaged devices automated reconnaissance is designed to find. They miss the patch schedule. They slip past vulnerability reports. And the people responsible for them have often moved on.
Microsoft has tracked this for years. In its 2024 Digital Defense Report, more than 90% of ransomware attacks that reached the actual ransom stage involved unmanaged devices on the network.
Makes sense.
Most systems IT actively manages will get patched eventually. The real risk lives in the systems no one is watching.
So here’s a practical ask: walk your network honestly. Look past the inventory on paper to what’s actually connected. The gap between those two pictures is your real exposure risk.
Getting a Read on Tarot
You may have seen us start to talk about Tarot. It’s a platform, but more than that, it’s a philosophy. It works by stitching asset intelligence, vulnerability data, threat context and business risk into one prioritized view.
Tarot is reading risk for our clients today, we continue to add new connectors and deepen the capabilities of it's core engine. The philosophy is clear: find what you have, see what’s exposed and prioritize the fixes by order of importance.
The Bottom Line
Mythos and its fellow AI platforms are changing the speed of the game. But the rules remain the same. And that makes these fundamentals more important than ever.
Need a little help?
Our team can help you map what’s actually on your network and build a plan to bring it under control.